/ THE SHORT ANSWER
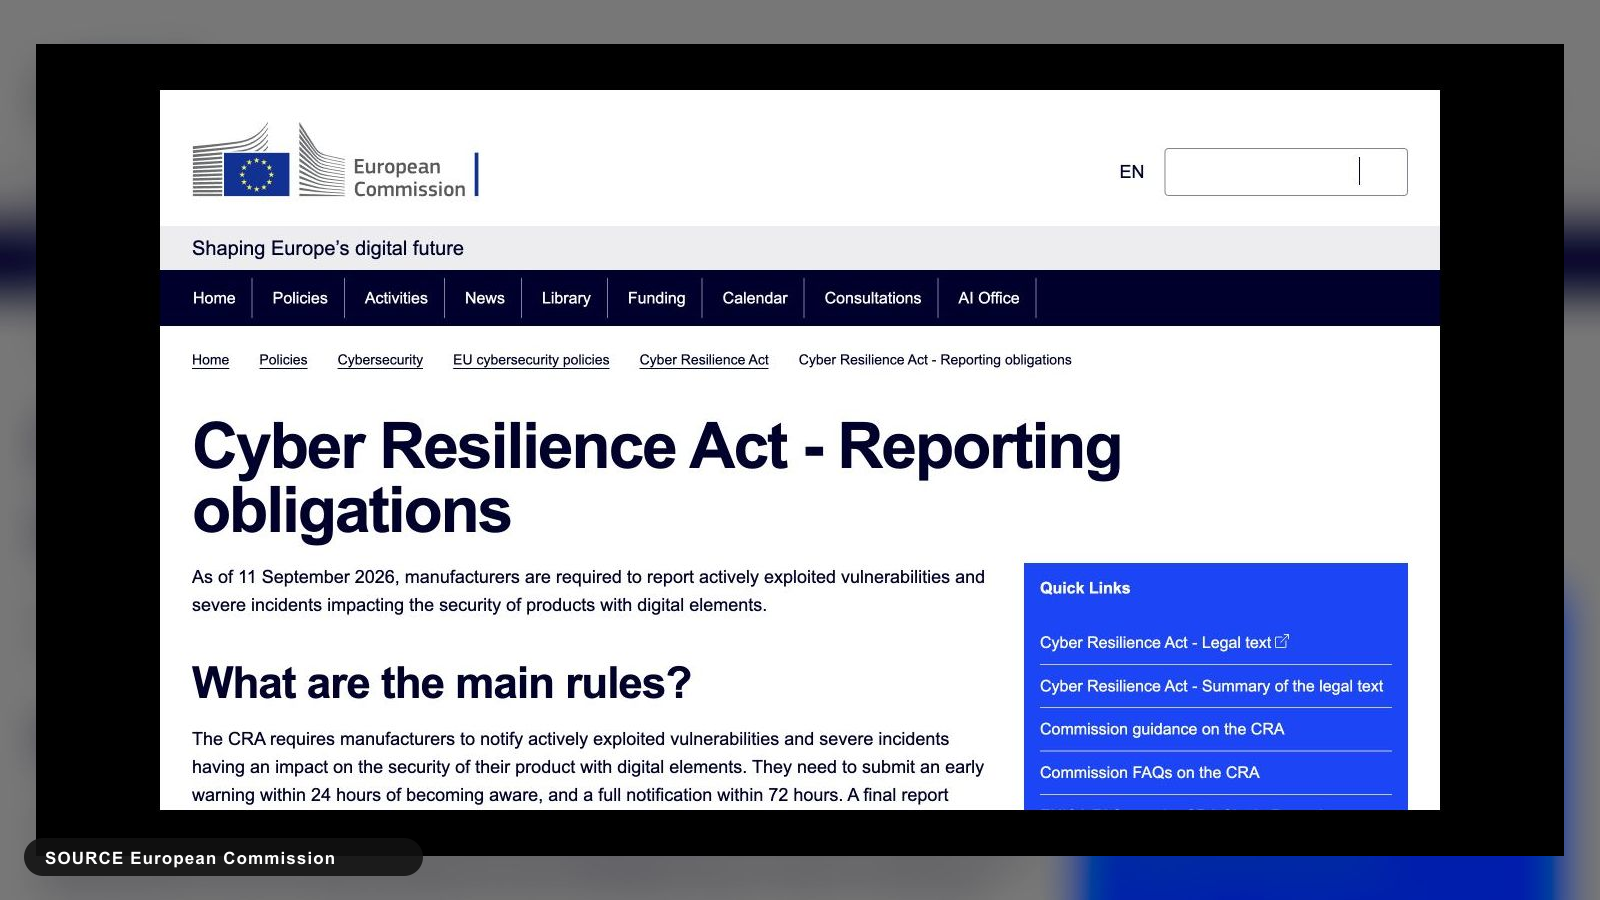
- 01Reporting duties begin on 11 September 2026.
- 02An early warning can be required within 24 hours and a fuller notification within 72 hours.
- 03The reporting trigger depends on active exploitation or a severe product-security incident.
- 04Teams need a documented cross-functional decision process before an incident occurs.
/ dotSuper point of view
The immediate CRA requirement is an incident-reporting operating process, not a last-minute paperwork exercise or a blanket vulnerability-scanning deadline.
What starts on 11 September
Reporting runs through the Single Reporting Platform established by ENISA.
The obligation arrives before the CRA’s broader product requirements apply in December 2027.
Companies should therefore avoid treating the September date as the deadline for every technical control in the regulation.
- Early warning within 24 hours of awareness
- Full notification within 72 hours
- Final report after corrective action for an exploited vulnerability
- Final report within one month for a severe incident
Build the reporting decision path
The organization needs one intake path and a named group able to determine whether the legal trigger is met.
Document when awareness begins, what evidence was available, who made the decision, and why the event was or was not reportable.
That record supports consistent decisions under time pressure.
- Identify the legal manufacturer for each EU product
- Map products and versions to owners
- Create a 24-hour legal and security escalation route
- Pre-authorize access to the reporting platform
Prepare the evidence package
Preserve affected versions, exploitation indicators, timelines, observed impact, mitigations, and contact details in a structured incident record.
Connect product security, incident response, engineering, legal, communications, and customer support.
Each team should know what evidence it owns and who can approve an external notification.
- Product name, version, and EU market footprint
- Known exploitation or incident evidence
- Impact and affected users or systems
- Containment, remediation, and disclosure status
What this page cannot conclude
- 01This article is operational guidance, not legal advice.
- 02Whether an event is reportable depends on the facts, product role, and applicable law.
- 03Organizations should use the latest Commission, ENISA, and national CSIRT guidance.
Sources
- 01Cyber Resilience Act reporting obligationsEuropean Commission · accessed Sep 10, 2026
- 02Single Reporting PlatformENISA · accessed Sep 10, 2026
- 03Cyber Resilience Act reporting obligationsNational Cyber Security Centre Ireland · accessed Sep 10, 2026
Our editorial standard · Found an error? Send a correction with its source.
/ CITE OR SHARE THIS GUIDE
Make the evidence easy to verify.
When you reference this guide, link to its canonical URL. That gives readers one stable place for the evidence, limitations and future updates.
dotSuper Research Desk. (September 10, 2026). EU Cyber Resilience Act Reporting Starts 11 September: A 24-Hour Readiness Checklist. dotSuper. https://dotsuper.net/feeds/daily-briefing/2026-09-10-eu-cyber-resilience-act-reporting-deadline